Who Controls the Infrastructure?
Every VPN server is rented hardware in a building someone else owns. Follows the chain from your device to the disk, and what real seizure cases revealed.
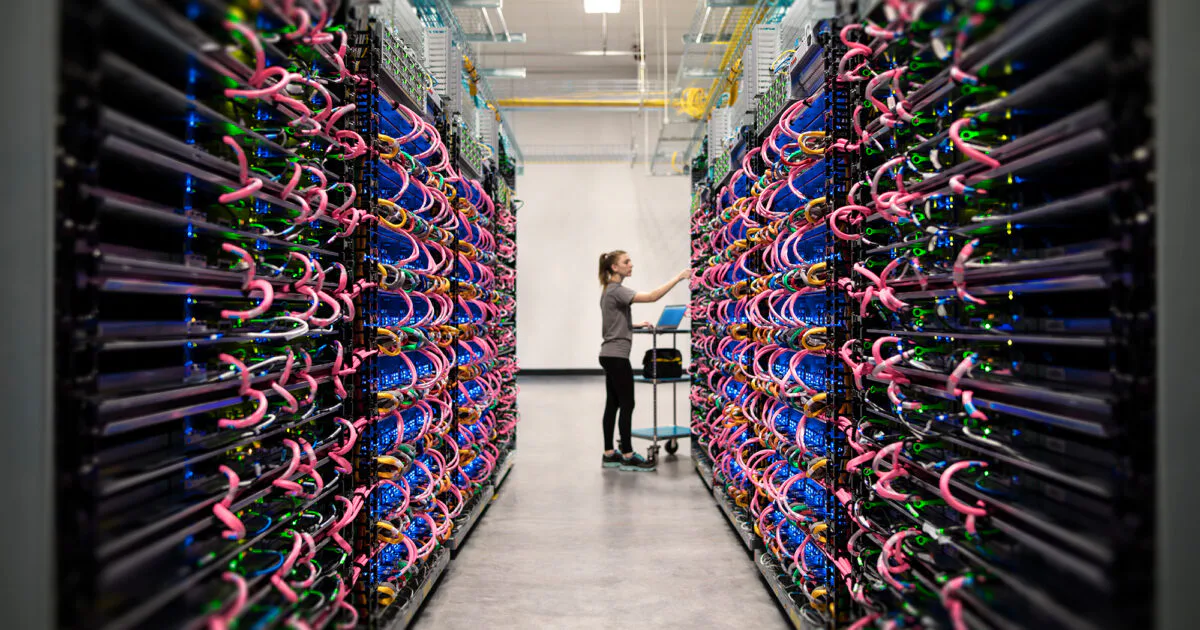
A VPN server is a computer in a rack, in a building, on a power circuit, connected to a network operated by somebody else. Whichever provider you pay, that chain is rented at every link. It matters because the question “can my provider see me” has a different answer from “can anyone get at my provider’s disk”, and only the second one has ever been tested in court.
Short answer#
Control follows the hardware. A provider can promise anything in a privacy policy and still lose the argument if the machine sits in a jurisdiction its owner cannot refuse, on infrastructure whose operator can be compelled separately. The practical consequence is simple: where the server is decides how much the policy is worth.
The chain from your device to the disk#
Four parties stand between your traffic and a disk you cannot inspect.
You pay a service. That service rents machines, either directly from a hosting provider or from a datacentre operator who rents space and power. The datacentre connects to transit and peering networks. At each step somebody else can act: the service can be compelled, the hosting provider can be compelled, the datacentre operator can be raided.
The first-order effect, that whoever runs the server can see both ends of your connection, is covered in What Is a VPN?. This article is about the second-order effect, which is that the same party may not be the one holding the hardware when someone comes with a warrant.
The same test, opposite outcomes#
Physical seizure is the closest thing the industry has to a controlled experiment. Investigators take the machine and look at what is actually on it. Four well-documented cases make the point better than any policy comparison.
ExpressVPN, Istanbul, January 2017. Turkish investigators were tracing the deletion of messages from the accounts of the police officer who assassinated the Russian ambassador to Turkey, and the trail led through an ExpressVPN exit address. The server was seized from the datacentre. It held no customer connection logs. ExpressVPN’s statement says the seizure occurred before they were contacted, and that the investigators’ inspection confirmed the company had nothing to hand over.
IPVanish, 2016. Homeland Security Investigations traced an IP to Highwinds Network Group, which owned IPVanish at the time. The first summons was answered with a refusal, on the grounds that no usage logs existed. A second, more detailed request produced a username, a full name, an email address, an IP address and the connection logs for one user. The user was traced to Muncie, Indiana, and arrested.
PureVPN, 2017. The provider handed connection logs to UK authorities in the Ryan Lin case. PureVPN’s privacy policy now states explicitly that it logs no browsing activity, connection timestamps, original IPs or DNS queries, and separately describes a deployment option that permits logging when instructed by authorities.
Perfect Privacy, Rotterdam, August 2016. Dutch authorities seized a server. Perfect Privacy confirmed no customer data was obtained.
Four seizures. Two produced nothing. Two produced an identity. The variable was never the protocol or the price tier.
Why “no activity logs” is not the same as no logs#
The IPVanish case is the one worth understanding, because the provider was not lying in the way the story usually assumes.
Connection logs and activity logs are different things. An activity log records what you did. A connection log records that an account with a given internal IP was active at a given time, which is enough to align one person with one session. The IAPP analysis of these cases puts it plainly: the information that broke both investigations was connection metadata, not browsing history.
This is the same distinction privacy versus anonymity draws, applied to an uncomfortable corner of the industry. A provider can state truthfully that it records nothing about what you did and still hand over everything needed to work out who you are.
The honest version of a no-logs claim is therefore specific. Mullvad’s policy lists what it does not keep, down to connection timestamps and DNS requests. PureVPN’s policy, as above, is careful about the gap. Those two pages are doing something different from a marketing sentence.
Who owns the building#
Placing a server in a country you cannot influence is a liability no policy can offset, and one provider has documented learning this the hard way.
After the 2017 seizure, ExpressVPN stopped operating physical servers in Turkey and switched the Turkish location to a virtual one, serving a Turkish IP address from hardware in the Netherlands instead. Users see no difference. What changed is which country’s authorities can walk into the datacentre.
The broader pattern is that most large providers rent from third-party hosting and cloud providers, and some publish little about which. Where a provider discloses its datacentre operators, that disclosure is the most useful single document it publishes, because it tells you which governments can reach the hardware.
Self-hosting as the third option#
The third option is to remove the provider from the chain, and it is a real one.
Running the server yourself means no operator sits between your traffic and the disk. It also means you own the patching, the uptime, the abuse complaints, and every configuration mistake. WireGuard is the usual choice here precisely because a small protocol surface is what makes that ownership realistic.
Self-hosting also removes your only advantage as a customer. When something breaks at 2am, you are the support desk, and no amount of structural independence substitutes for someone else holding the pager.
How to check for yourself#
Three checks are cheap and rarely done.
Ask who owns the company behind the brand, then follow commercial versus independent VPNs for what that structure can and cannot promise.
Ask whether the provider publishes a transparency report counting legal requests received, requests judged valid, and requests answered with data. IVPN’s report lists 34 requests received between 2016 and 2026, three judged valid, and none answered with data.
Ask what happens if the hardware is seized. If the answer is only a policy, the seizure cases above are your reference.
Common misconceptions#
“RAM-only servers make seizure pointless.” A diskless machine has nothing to seize, which helps. It does nothing about a compelled request to the operator, and it does nothing about connection metadata that never touches the disk.
“The provider’s jurisdiction is enough.” Jurisdiction binds the company. The hardware may sit somewhere else, and the datacentre operator answers to its own government.
“A transparent network is not a transparent operator.” Showing users the exit IP list describes your product, not your legal exposure.
“Self-hosting is strictly safer.” It removes one party and adds several duties, including ones you cannot delegate.
Related#
- Commercial VPN vs Independent VPN: who owns the company above this chain
- What Is a VPN?: the first-order effect of the tunnel itself
- What Should You Look for in a VPN?: the decision procedure this article supports
- Privacy vs Anonymity: why connection metadata can identify you
Sources
Last reviewed October 8, 2026. Corrections and additions are welcome.